MFA Isn’t Enough Anymore: How New Phishing Kits Are Getting Past Multi-Factor Authentication in Education and Government
Share this post
Author
If your organization has multi-factor authentication (MFA) turned on for Microsoft 365, you have already done more than most. But a new wave of phishing kits and threat infrastructure is proving that a completed MFA prompt no longer guarantees a legitimate sign-in — and schools, colleges, and government agencies are squarely in the blast radius.
Two months ago, we wrote about Iranian state-sponsored actors shifting from destructive attacks toward quieter credential theft. The September update to our Guardian 365 IOC Feed continues that story, but with a twist: the tools doing the damage now aren’t limited to nation-state actors. Commercial phishing-as-a-service kits, available to anyone with a Telegram account and a few hundred dollars, are using the same tricks to get past MFA on the Microsoft 365 sign-in page — the front door nearly every education and government organization relies on every day. Here is what changed, why it matters if your organization runs on Microsoft 365, and what Guardian 365 is doing about it.
Why This Matters for Education and Government
Attackers don’t need a new vulnerability when they can walk through the front door with a valid login. This release pairs Iranian-affiliated infrastructure identified by the Cybersecurity and Infrastructure Security Agency (CISA) with commercial phishing kits built specifically to defeat MFA — and both point squarely at the institutions we work with every day.
- The CISA advisory covers organizations that run industrial control systems, and that includes plenty of campuses and county facilities managing water, energy, and building automation equipment.
- The phishing-kit campaigns name universities directly. Threat intelligence firm Infoblox lists universities among the top targets of one campaign, and Arctic Wolf lists education and government among the sectors hit hardest by another, known as Payroll Pirates.
- Every school district, college, and agency runs payroll and procurement — and the staff who manage those processes hold real financial authority, often with the account permissions and process exceptions that come with that responsibility.
Four Threat Clusters Behind the September Indicators
Our Guardian 365 SOC reviewed threat intelligence from CISA, the FBI, Arctic Wolf, Infoblox, and Huntress to build this release. Four distinct clusters stood out.
1. Iranian-Affiliated Infrastructure Targeting Operational Technology
CISA’s advisory AA26-097A describes Iranian-affiliated actors, linked to earlier activity by the IRGC-affiliated group CyberAv3ngers, exploiting internet-exposed industrial control systems across U.S. water, energy, and government facilities. Thirteen IP addresses tied to this activity are included in this release. If your organization operates building automation, water, or energy control systems, it’s worth reading the full advisory — its guidance on remote access and default credentials applies just as much to campus and municipal facilities as it does to utilities.
2. Kali365: A Phishing Kit That Rents for $250 a Month
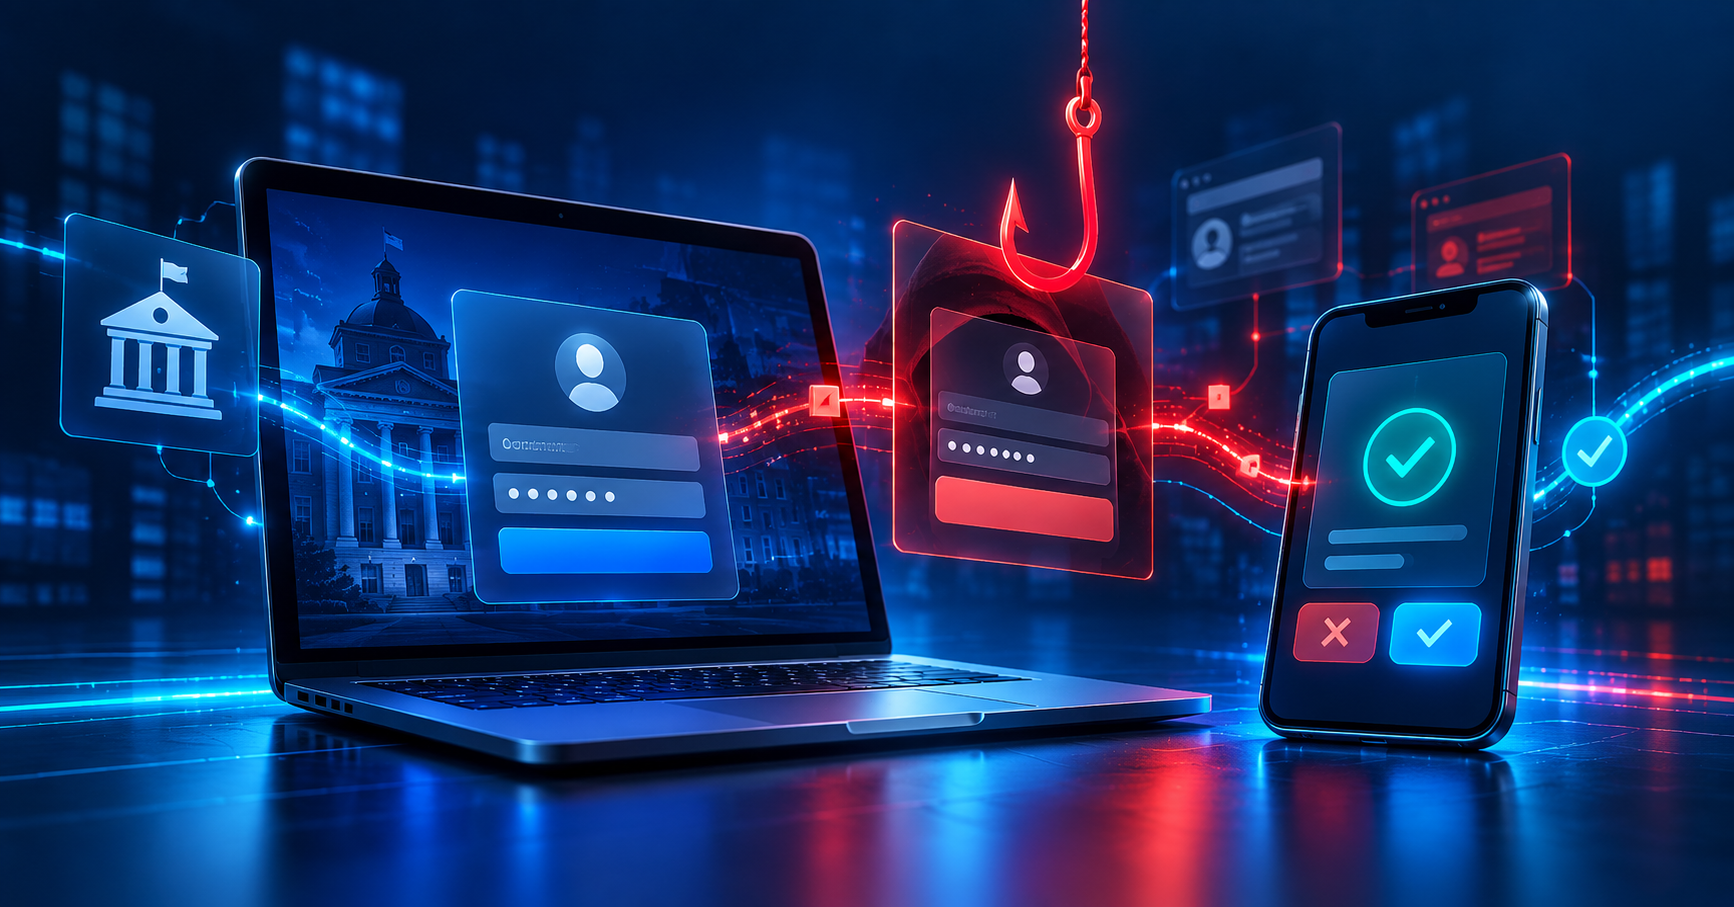
Kali365 launched in April 2026 and sells on Telegram for roughly $250 a month — no advanced hacking skills required. It exploits Microsoft’s device code sign-in flow, the same process used to sign in to a smart TV or streaming device. The attacker starts a sign-in on their own machine, generates a legitimate short code, and a phishing email convinces the victim to enter that code on the real Microsoft sign-in page. The victim completes their own MFA prompt — on the genuine site — and unknowingly hands the attacker an active session. According to security firm Huntress, the stolen access can outlive a password change.
3. Payroll Pirates: When MFA Succeeds and the Attacker Still Wins
This cluster, documented by Arctic Wolf in August, starts with a fake voicemail notification email. The link leads to a lookalike Microsoft sign-in page that sits invisibly between the victim and the real Microsoft 365 service — a technique called adversary-in-the-middle (AiTM). The fake page relays the victim’s password and MFA response to Microsoft in real time, lets the sign-in succeed, and quietly keeps the session for itself. From there, attackers search for payroll, HR, and finance staff and, in some cases, add inbox rules that hide their tracks.
4. The Procurement Trap: Fake Vendor Documents on Real Websites
Since at least May, a campaign identified by Infoblox has targeted universities and public agencies with procurement-themed emails sent from previously compromised accounts. The links lead to convincing fake document pages, hosted on legitimate but compromised websites, that ultimately steal Microsoft 365 credentials and sessions. A CAPTCHA step keeps automated security scanners from ever seeing the malicious page behind it.
What These Threats Mean for Your Organization
MFA is necessary — but it’s no longer sufficient on its own. Device code phishing and AiTM proxies both let a victim complete a real MFA prompt without ever realizing anything is wrong. What actually stops these techniques is phishing-resistant authentication (like security keys or passkeys), sessions tied to a trusted device, and blocking sign-in methods your organization doesn’t use.
These lures look like they come from someone you trust. Every campaign in this release sends its next wave of phishing emails from an already-compromised mailbox or hosts its fake page on an established, previously trustworthy website. That’s exactly why layered detection — not just a strong password policy — matters.
Behavior is the tell. A new inbox rule, a sign-in from an unexpected location, an unfamiliar app pulling data through Microsoft Graph — these are the signals that give attackers away, and they’re exactly what a well-tuned threat detection service like Guardian 365 is built to catch.
63 New Indicators Added to Guardian 365
Our SOC checked every indicator in this release against 30 days of endpoint, email, identity, and cloud-app telemetry across the Guardian 365 customer community before assigning an action. We found no matches — meaning these threats haven’t shown up yet in the environments we monitor — so nearly all indicators move straight to active blocking rather than sitting in an alert-only queue.
| Indicator Type | Count | Action |
| IPv4 addresses | 17 | Block |
| Domain names | 45 | Block |
| File hash (SHA-256) | 1 | Block and remediate |
These 63 indicators break down as: 13 IP addresses tied to the CISA advisory, 21 tied to the Kali365 kit and its supporting tools, 7 Payroll Pirates domains, 18 from the procurement campaign, and 4 domains linked to a VPN provider recently sanctioned by the U.S. Treasury for supporting ransomware operators.
How Guardian 365 Is Responding
Guardian 365 customers enrolled in the IOC Feed will have these indicators deployed automatically across their environment starting Friday, September 25, with a deployment confirmation to follow. No action is required on your part — that’s the point.
Not yet enrolled in the IOC Feed? Reach out to your Customer Success Account Manager (CSAM) to get started.
Not a Customer Yet? Get Protected.
These threats differ in sophistication, motive, and price of entry — from a nation-state actor to an anonymous kit reseller on Telegram — but they all converge on the same target: a Microsoft 365 sign-in page that looks legitimate because, technically, it is.
You don’t have to figure out your exposure alone. A free Guardian 365 security assessment gives you a clear picture of where your Microsoft Entra ID, Microsoft Defender XDR, and Microsoft 365 posture stands against exactly these techniques — and what to prioritize first.
Email info@forsyteit.com to get started.
We Make Security Easy.
Ready to make security easy?
Find out where your organization stands. Our free security assessment gives you a clear picture of your current posture and a roadmap for what comes next.