When a Phone Call Becomes a Data Breach: The Technical Anatomy of the McKesson Vishing Attack
Share this post
Author
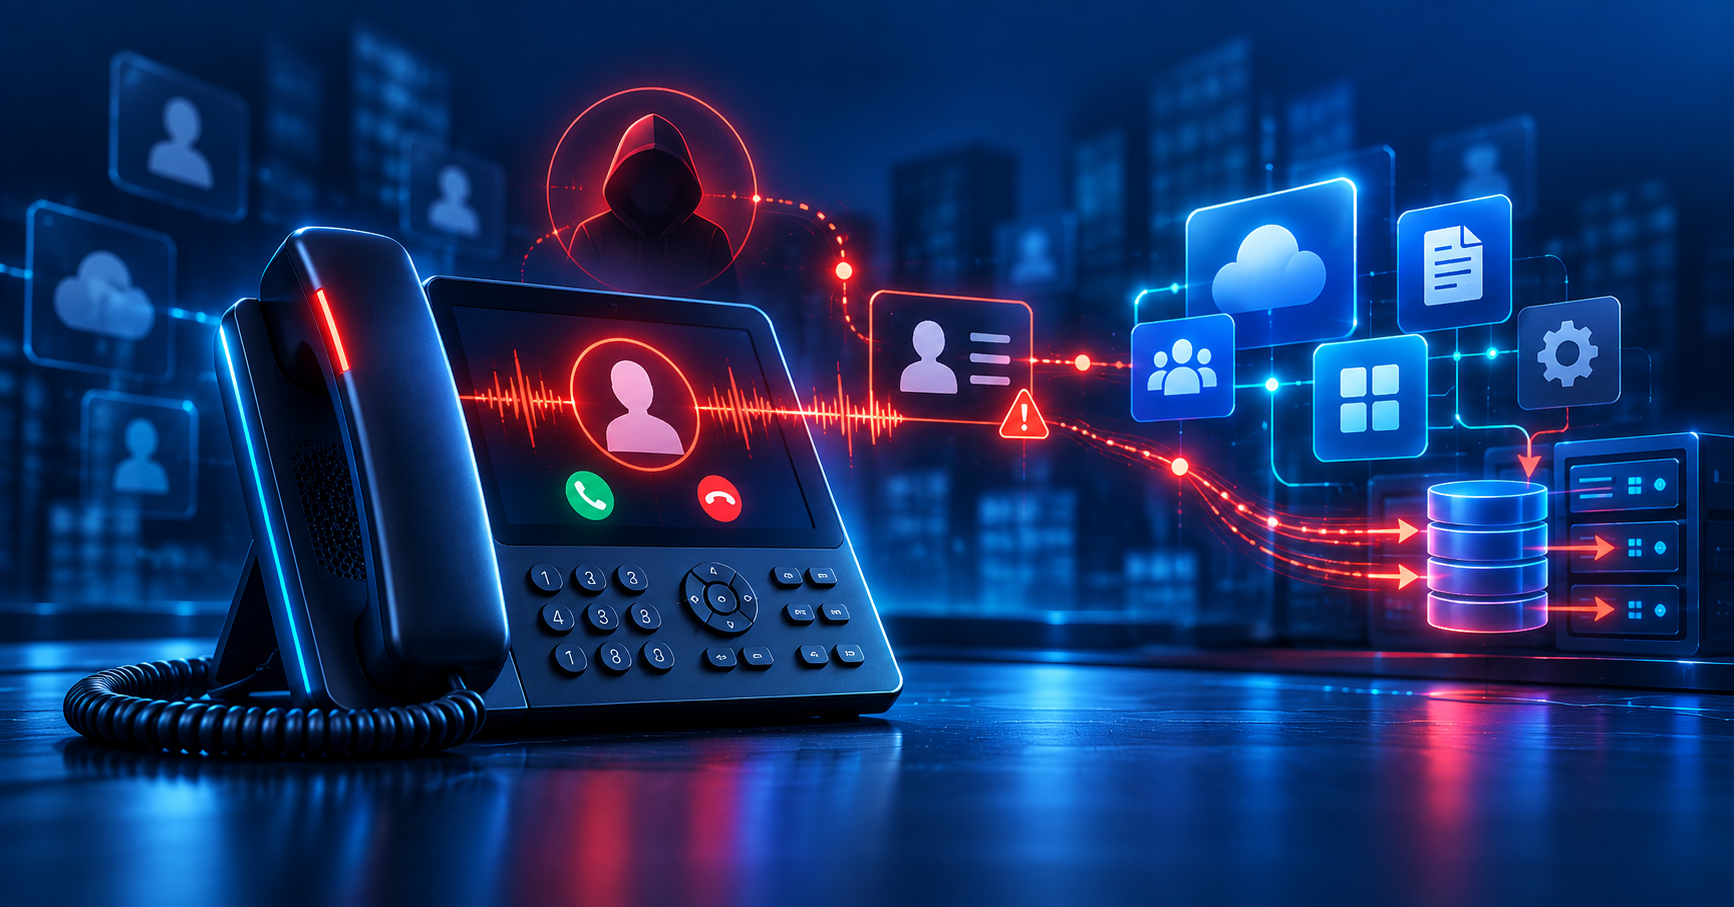
No exploit. No malware. No unpatched server. Somewhere inside McKesson Corporation this past August, an employee picked up the phone, believed the person on the other end was calling from IT, and did exactly what they were asked to do.
That’s reportedly how one of the largest healthcare and pharmaceutical distribution companies in the country disclosed a cybersecurity incident involving unauthorized access to internal systems and data theft. The extortion group ShinyHunters publicly claimed responsibility, describing a voice-phishing (“vishing”) campaign that bypassed employee identity verification and reached Salesforce and Snowflake, reportedly after first compromising Okta single sign-on access.
For education and government IT teams running Microsoft 365, Entra ID, or any identity-federated SaaS stack, the value here isn’t the headline — it’s the attack chain underneath it. Here’s a technical breakdown of how this class of attack works, how it maps to MITRE ATT&CK, and what to hunt for and harden right now.
The Reported Attack Chain
Public reporting describes a five-stage sequence security teams are seeing more often across sectors:
- Pretext and initial contact. The attacker calls a targeted employee posing as internal IT. This bypasses email gateways and URL filtering entirely, since the attack happens over a voice channel with no artifact for traditional tooling to inspect. A supporting lookalike domain was also reportedly used to reinforce the pretext or harvest credentials.
- Identity compromise via Okta SSO. Rather than harvesting a static password, this style of attack typically targets the identity session itself, through MFA fatigue/push bombing, adversary-in-the-middle credential relay, or social-engineered enrollment of an attacker-controlled MFA method that survives a password reset.
- Lateral movement into federated SaaS. Once inside the identity provider, the attacker inherits access to every downstream application connected through SSO — in this case, reportedly Salesforce and Snowflake. This stage is often the least monitored, because the activity uses legitimate, authenticated sessions rather than malware.
- Data staging and exfiltration. Authenticated access to a CRM or data warehouse allows bulk export via native features or APIs, often over standard HTTPS that rarely triggers network-layer alerting on its own.
- Extortion. The incident becomes public once the threat actor lists the organization on a leak site or issues a ransom demand — by which point the earlier stages generated few, if any, high-fidelity alerts.
MITRE ATT&CK Mapping
Mapping the reported chain to ATT&CK turns this incident into concrete detection priorities:
- T1566.004 – Phishing: Spearphishing Voice (the vishing pretext)
- T1621 – MFA Request Generation (push bombing)
- T1556.006 – Modify Authentication Process: MFA (attacker-controlled MFA enrollment)
- T1078.004 – Valid Accounts: Cloud Accounts (legitimate identity used for access)
- T1550.001 – Use Alternate Authentication Material: Application Access Token (session/token reuse across SaaS)
- T1567.002 – Exfiltration Over Web Service: Cloud Storage (bulk data export)
What to Hunt For
- Identity provider: new MFA method registrations followed by sign-ins from unfamiliar devices or geographies; spikes in MFA push notifications to a single user; sign-ins that pass Conditional Access but originate from an unusual ASN; help desk resets not tied to a verified ticket.
- SaaS/data platforms: unusual login-to-export time; Salesforce spikes in bulk exports or permission-set changes; Snowflake anomalous query volume against PII/PHI tables or new roles/warehouses outside change control; unapproved new OAuth app connections.
- Network/endpoint: large outbound HTTPS transfers to unapproved cloud storage domains; DNS queries to newly registered or lookalike domains.
Entra ID sign-in logs — filter: Authentication requirement = multifactor AND Result = success AND Client App != previously seen for user
Hardening Priorities
- Move to phishing-resistant authentication. Passkeys and Windows Hello for Business remove the shared secret and push-approval step vishing depends on — prioritize help desk, HR, finance, and SaaS-connected staff.
- Add out-of-band verification to help desk workflows. Require a callback, ticket reference, or manager confirmation before any MFA reset or device registration.
- Apply Conditional Access token protection and sign-in risk policies, and enable Continuous Access Evaluation (CAE) for near-real-time access revocation.
- Extend monitoring into SaaS applications. Ensure Salesforce, Snowflake, and similar platforms feed authentication and export activity into your SIEM/XDR, not just your identity provider.
- Establish behavioral baselines for data platforms. A “technically authorized” export can still be abnormal — behavioral analytics catches what access control alone won’t.
Why Education and Government Should Treat This as a Blueprint
- The pretext is universal. Every school district, college, and agency runs a help desk trained to be responsive first, skeptical second.
- The identity fabric is the same. Entra ID, Google Workspace, and SSO-connected SaaS create the same lateral-movement path, regardless of sector.
- The blast radius is architectural. Any organization federating identity across CRM, ERP, or data-warehouse platforms shares this exposure.
How Guardian 365 Helps
Guardian 365 monitors identity, endpoint, email, and cloud-app signals across the Microsoft ecosystem around the clock, correlating the exact indicators above — new MFA registrations, anomalous sign-ins, unusual data movement — so a compromised identity is caught before it becomes an exfiltration event and a headline.
Not yet enrolled in Guardian 365 threat monitoring? Reach out to your Customer Success Account Manager (CSAM) to review your identity security posture and SaaS monitoring coverage.
Protect Your Organization Before the Call Comes In
A free Guardian 365 security assessment gives you a clear picture of your Microsoft Entra ID, Microsoft Defender XDR, and Microsoft 365 posture against attacks like this one — and a prioritized plan for closing the gaps that matter most.
Email info@forsyteit.com to get started.
We Make Security Easy.
Ready to make security easy?
Find out where your organization stands. Our free security assessment gives you a clear picture of your current posture and a roadmap for what comes next.